

Thirteen scanners. One dashboard.
Every asset you own is checked by all 13 scanners on every plan — no scanner is hidden behind a higher tier. AI explains every finding in plain English so the smallest teams can act without a security specialist on staff.
Port & service scanning
Nmap-powered discovery of open ports, running services, and banner-level version detection across every IP you own.
CVE scanning (Nuclei)
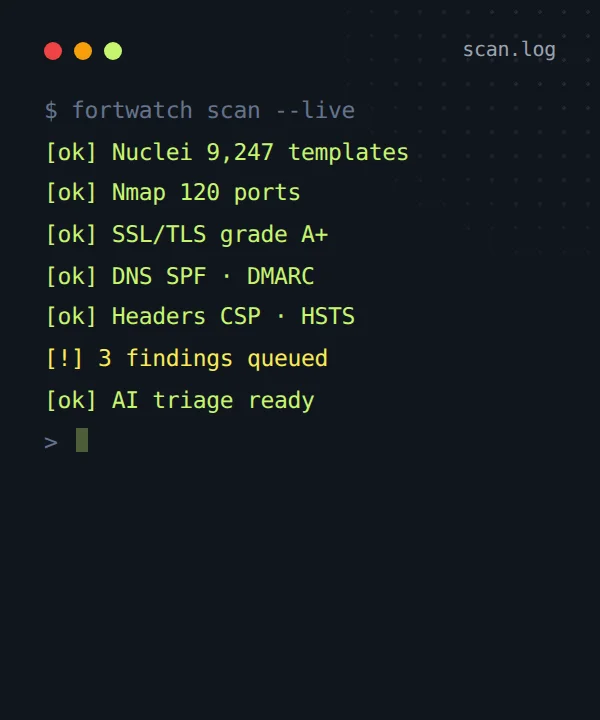
9,000+ Nuclei templates run continuously against your assets — from critical RCEs to misconfigurations, with fresh templates pulled daily.
SSL & TLS monitoring
Certificate expiry, chain validation, cipher strength, and TLS protocol grading via testssl.sh — with escalating alerts at 30/14/7/1 days.
DNS security
DNSSEC, CAA, and nameserver health checks plus dangling-record detection, so no one can hijack your domain or claim a forgotten subdomain.
HTTP security headers
CSP, HSTS, X-Frame-Options, CORS, and cookie flag analysis on every response — with concrete header values you can copy into your nginx or app.
Sensitive file detection
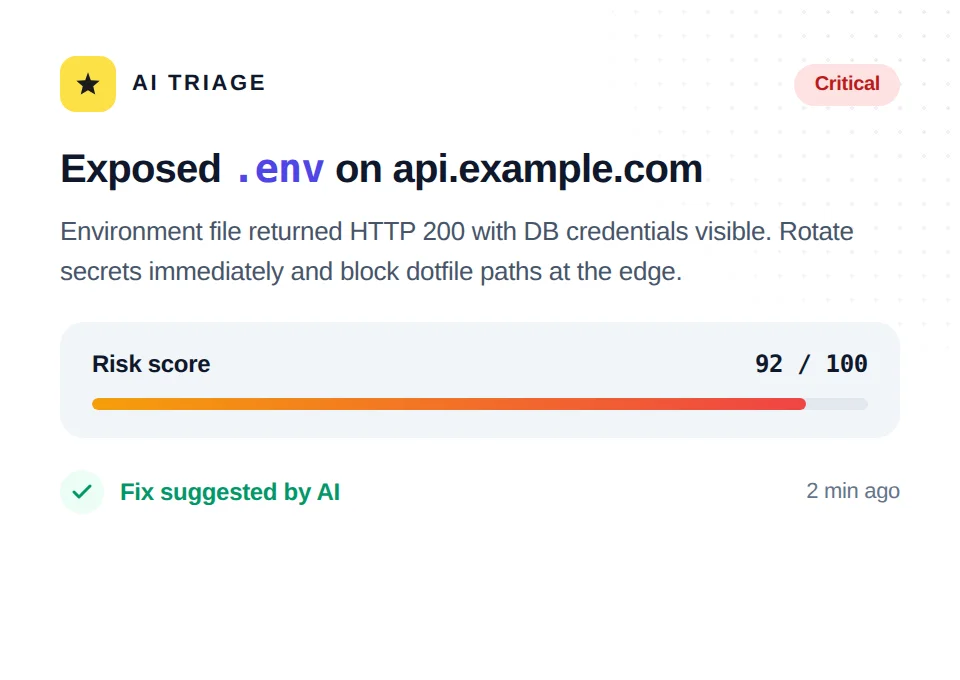
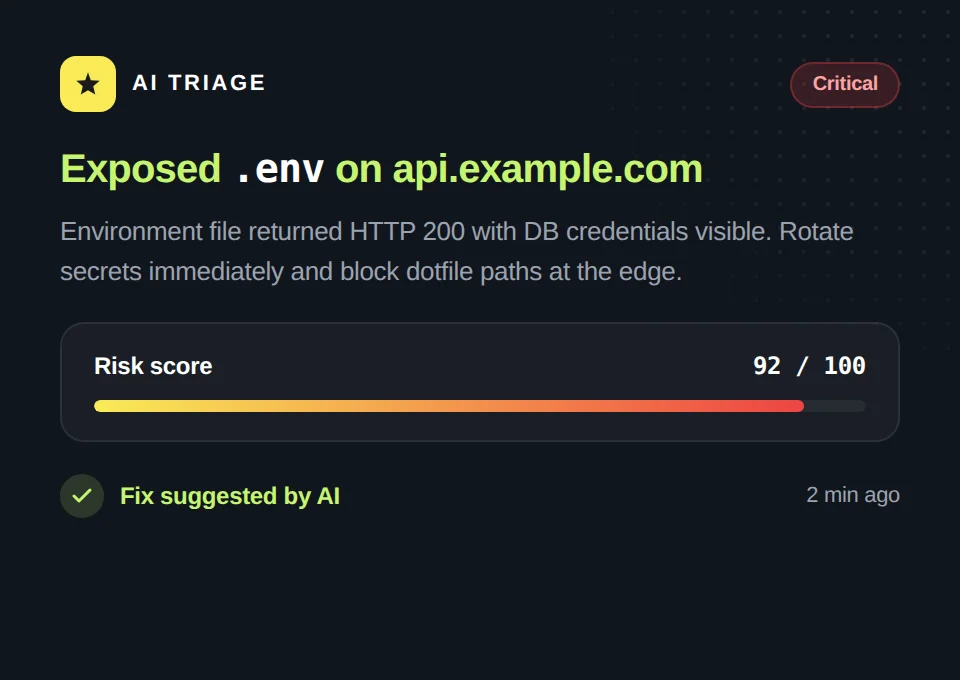
117 paths checked per asset: exposed .env, .git, backup SQL dumps, admin panels, phpinfo, debug endpoints — the things attackers look for first.
Subdomain takeover
Dangling DNS records pointing at unclaimed cloud services (Heroku, AWS, GitHub Pages, Fastly, 50+ fingerprints) — caught before someone else claims them.
Cloud bucket exposure
Public S3, GCS, and Azure Blob discovery from the outside. Find leaking buckets tied to your brand before a researcher or attacker does.
Brand & typosquat monitoring
Newly-registered lookalike domains that target your brand — catch phishing infrastructure before it goes live against your customers.
Screenshot & visual monitoring
Automated per-asset screenshots so you see how your assets look from the outside, and spot silent defacements or unexpected login pages.
Email authentication
SPF, DKIM, DMARC, and MX checks on every domain that sends mail, so attackers can't spoof your address or slip phishing into your customers' inboxes.
Technology fingerprinting
Detects the frameworks, servers, and runtimes behind every asset and flags end-of-life versions before a known CVE finds them.
WHOIS & domain expiry
The registry record of every domain, every scan: expiry at 90, 60 and 30 days, a missing transfer lock, and a registrar or nameserver change since the last run.
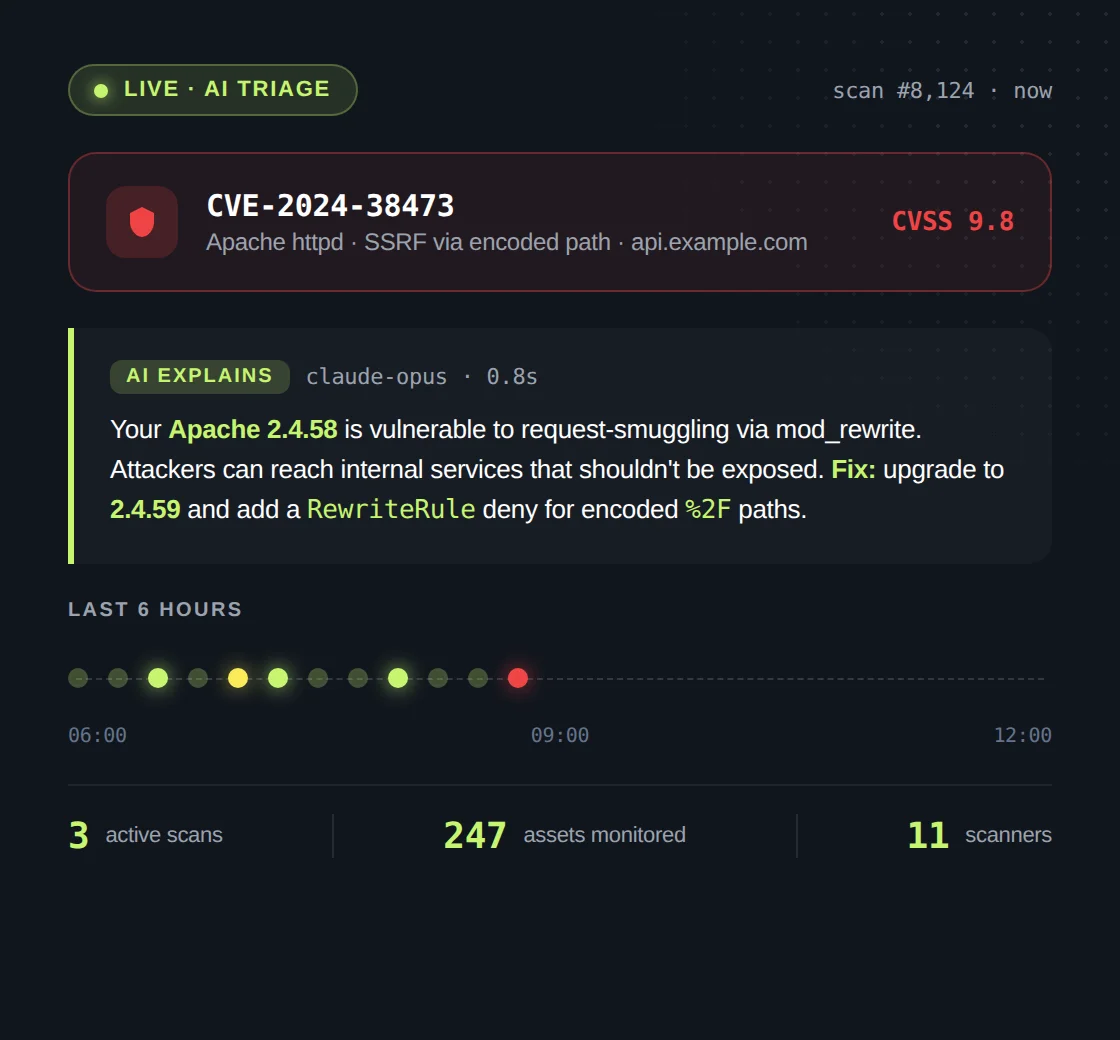
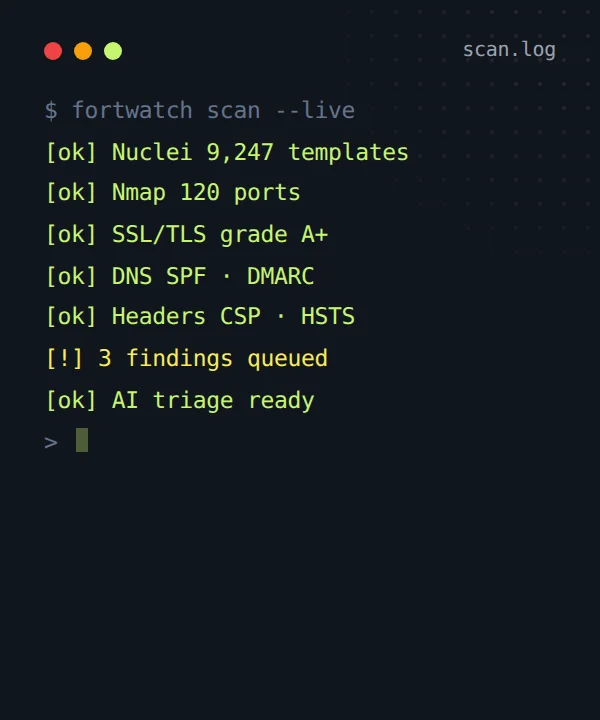
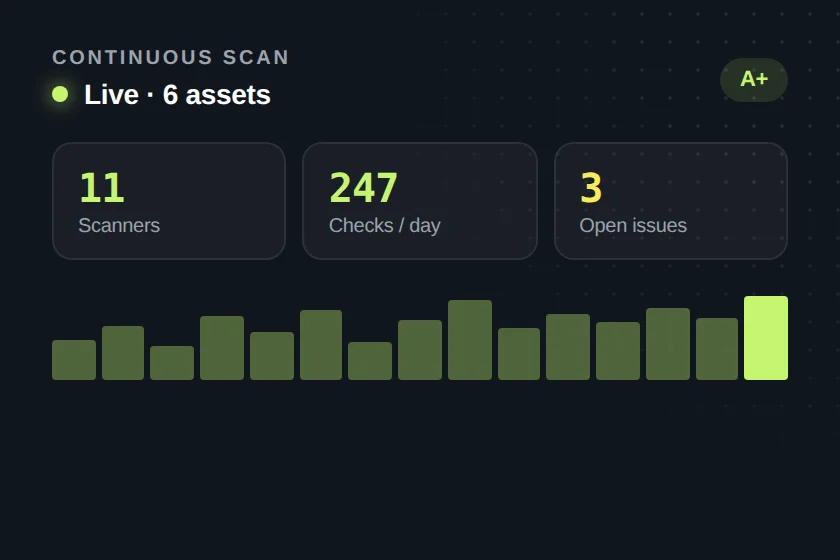
Continuous scanning, explained by AI.
- Add a domain and we start scanning in under 5 minutes.
- Scheduled scans catch new issues the moment they appear.
- AI explains every finding — no security degree required.
Enterprise-grade scanning, without the enterprise overhead
FortWatch protects the businesses its founder owns — every finding, every false positive, every confusing alert is a problem we feel first. The result is a scanner that respects your time and speaks your engineers’ language.
All scanners on every plan
AI-powered triage
Scheduled scans
All 13 scanners. AI on every plan.
Save 20% on annual billing. Every plan includes 5 infrastructure assets and 1 web app, AI analysis, and every scanner on this page — nothing hidden behind a higher tier.
Essential
For startups and small teams starting vulnerability management.
$99
/mo billed annually · 5 infra + 1 app
$124/mo monthly
- All 13 scanners on every asset
- AI-powered analysis on every finding
- Weekly scheduled scans
- 5 infra + 1 web app included
- Extra infra: $4/mo · extra app: $49/mo
- Up to 3 team members
- Email notifications
- Email support
Pro
For growing teams that need continuous protection and reporting.
$199
/mo billed annually · 5 infra + 1 app
$249/mo monthly
- Everything in Essential
- Daily scheduled scans + on-demand
- Emerging-threat CVE re-scans
- Port & service discovery (Nmap)
- PDF & CSV reports
- Slack, email, and webhook alerts
- Issue tracking with SLA deadlines
- Up to 10 team members
- Priority support
Business
For teams with compliance posture and deeper asset visibility.
$329
/mo billed annually · 5 infra + 1 app
$412/mo monthly
- Everything in Pro
- Cloud bucket exposure (S3, GCS, Azure)
- Subdomain takeover detection
- Brand & typosquat monitoring
- Sensitive file scanning (117 paths)
- Custom scan schedules per asset
- Extra infra: $6/mo · extra app: $59/mo
- Up to 25 team members
- Dedicated account manager
Need unlimited assets, SOC 2 evidence exports, or white-glove onboarding? Talk to us about Enterprise.
Ready to secure your infrastructure?
Start your free trial today and scan your entire attack surface in under 5 minutes.
No credit card required
7-Day free trial
Secure your entire stack today
Start scanning in under 5 minutes. No credit card required. 7-day free trial included.